AI Agent Mistakes: కిరణ్ Businessకి Automation ఎందుకు ఖరీదైంది?
AI agent పని చేస్తోంది అంటే business problem solve అయిందని కాదు. తప్పు processని వేగంగా నడిపితే, తప్పు కూడా వేగంగా పెరుగుతుంది.
గమనిక: కిరణ్, అతని colleague మేఘన, shop మరియు సంఘటనలు ఈ article కోసం సృష్టించిన fictional examples. ఇది నిజమైన client case study కాదు; savings లేదా business resultsకు హామీ కాదు.
“అన్నీ agent చూసుకుంటుంది” అన్న ఒక Monday morning
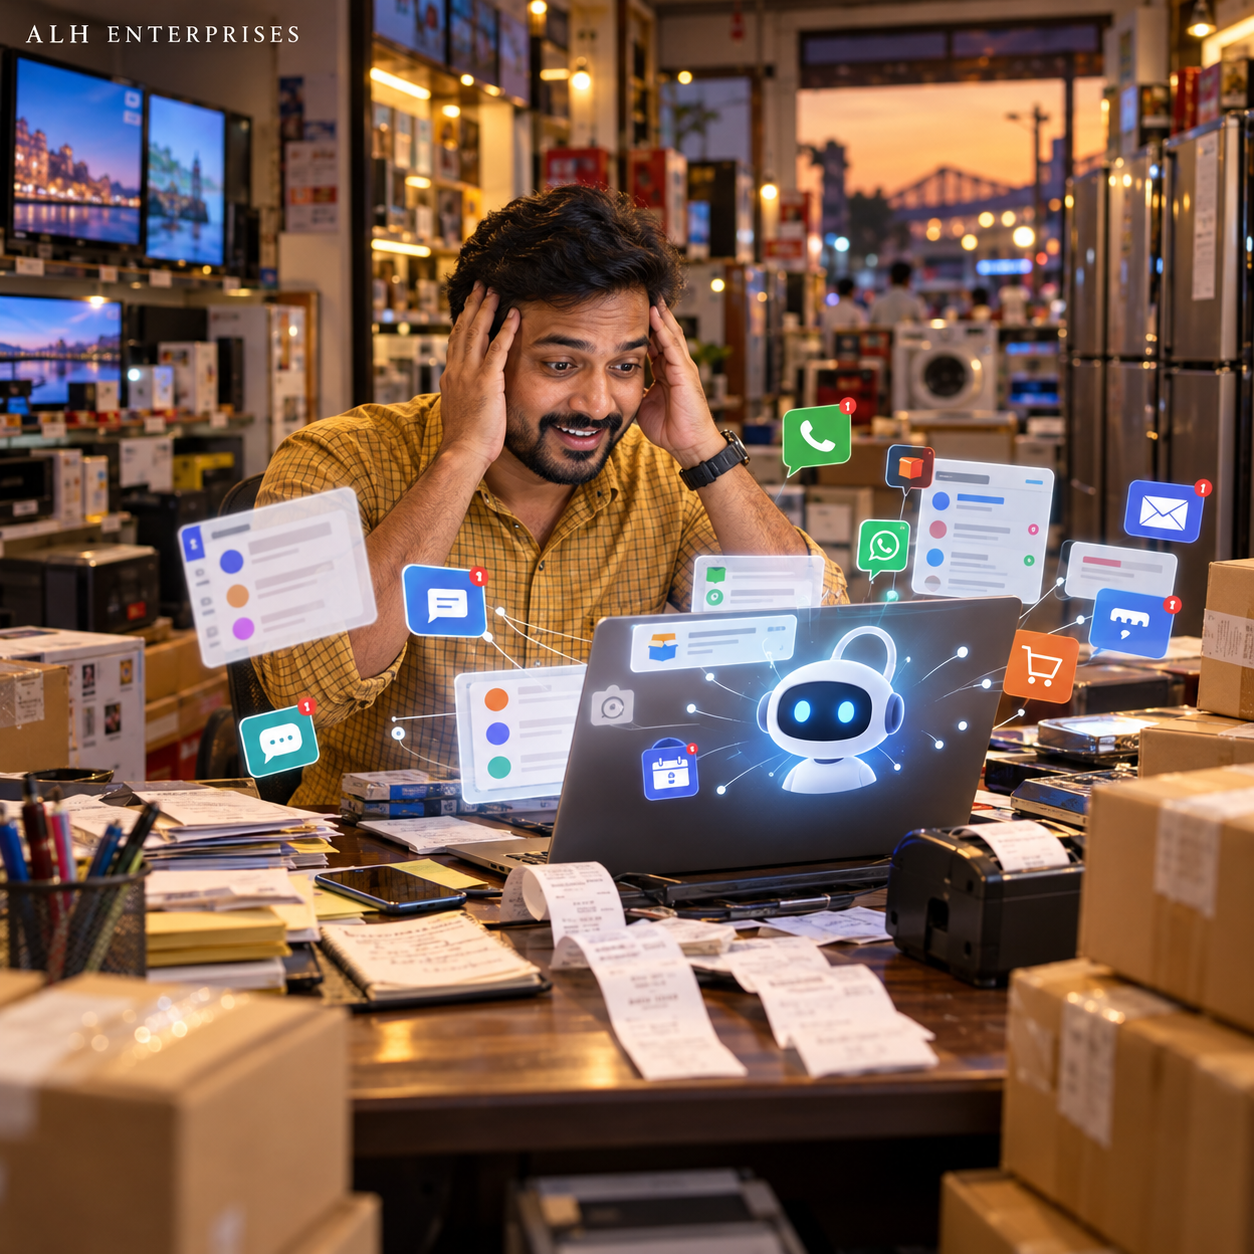
విజయవాడలో home appliances, electronics shop నడిపే కిరణ్కు రోజంతా ఒకే ప్రశ్నలు: “ఈ model stockలో ఉందా?”, “delivery ఎప్పుడు?”, “warranty ఎంత?”, “ఈరోజు price ఏంటి?” Calls, WhatsApp messages, counter customers—teamకి ఊపిరి ఉండేది కాదు.
ఒక demo చూసిన తర్వాత అతనికి solution కనిపించింది: AI agent. కానీ మొదటి నుంచే ఒక చిన్న task ఇవ్వకుండా, customer support, quotations, order confirmation, stock check, refunds—అన్నీ ఒకేసారి automate చేయాలని ప్రయత్నించాడు. ఒక weekలో agent live అయింది. Screen మీద replies వేగంగా వచ్చాయి. కిరణ్ ఆనందపడ్డాడు: “ఇక staff time save!”
కానీ busy work తగ్గలేదు. కొత్త పని పుట్టింది—agent చేసిన decisionsని వెనక్కి వెళ్లి సరిచేయడం.
Mistake 1: Toolతో మొదలుపెట్టి, problemను తర్వాత వెతకడం
కిరణ్ మొదటి mistake wrong use case. “AIతో ఏమేం చేయవచ్చు?” అని మొదలుపెట్టాడు; “మా businessలో repeat అయ్యే, low-risk bottleneck ఏది?” అని అడగలేదు.
ప్రతి process agentకు సరిపోదు. Rules తరచుగా మారే refund decisions, unusual complaints లేదా high-value ordersకు context, judgment అవసరం. కానీ approved product catalogue నుంచి FAQ answer ఇవ్వడం, lead details collect చేయడం, delivery-status requestని సరైన employeeకి route చేయడం—ఇవి narrower starting points.
NIST AI Risk Management Framework కూడా intended use, scope, expected benefits, costs మరియు human oversightను ముందే document చేయాలని సూచిస్తుంది. అందుకే కిరణ్ చేయాల్సింది “full shop automation” కాదు. మొదటి target ఇలా measurableగా ఉండాలి: verified catalogueలో ఉన్న basic questionsకు draft reply తయారు చేసి, employee approval తర్వాత మాత్రమే పంపడం.
Mistake 2: Smart agentకు messy data ఇవ్వడం
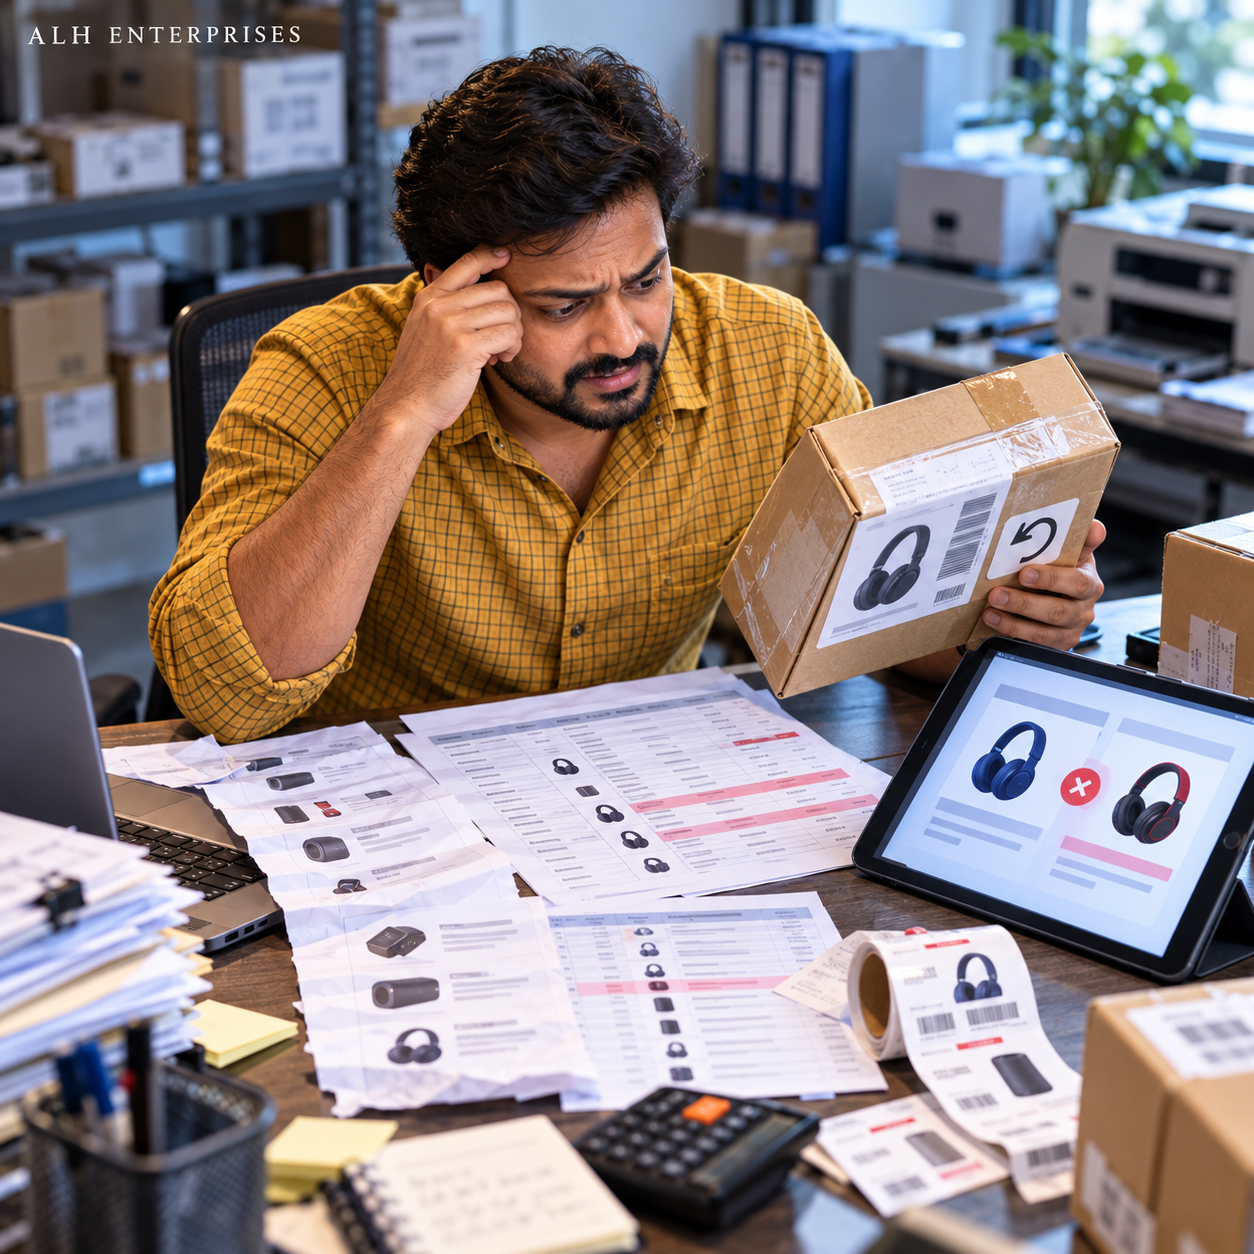
మంగళవారం మొదటి complaint వచ్చింది. Websiteలో old price, spreadsheetలో new price, WhatsApp listలో ఇంకో offer. ఒకే productకు మూడు names. Discontinued mixer ఇంకా “available”గా ఉంది. Agent తనకు కనిపించిన dataతో confident reply ఇచ్చింది—కానీ అది wrong.
AI agent quality, దానికి ఇచ్చే context మరియు tools qualityని దాటి magically పెరగదు. Incomplete, duplicate, outdated లేదా unstructured data ఉంటే wrong answers, hallucination-like confident errors, returns, rework రావచ్చు. కిరణ్ team save చేయాలనుకున్న ఐదు నిమిషాల reply, ఇప్పుడు apology call మరియు corrected invoiceగా మారింది.
మేఘన—shop operations చూసే fictional colleague—ఒక simple rule పెట్టింది: one approved catalogue, one owner, one “last updated” date. Missing field ఉంటే agent guess చేయకూడదు; “team confirmation needed” అని route చేయాలి.
Mistake 3: అవసరమైన access కంటే ఎక్కువ ఇవ్వడం
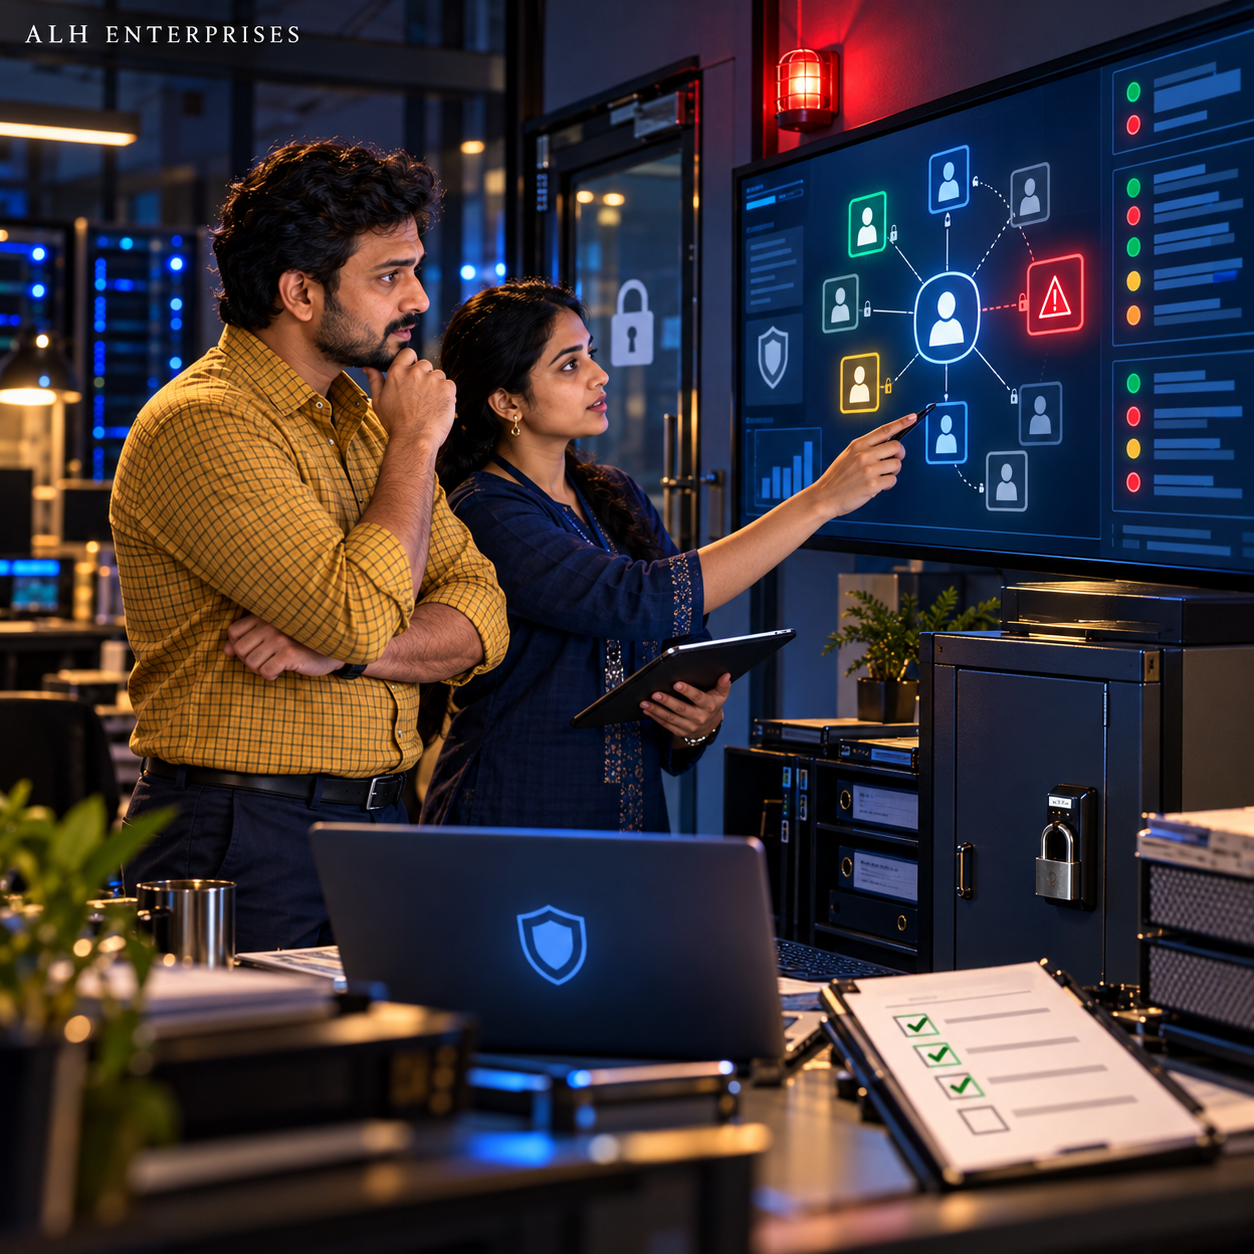
Speed కోసం కిరణ్ agentకి shared drive, order sheet, customer folder, edit permissions అన్నీ ఇచ్చాడు. “అది ఉపయోగించకపోయినా ఏమవుతుంది?” అనుకున్నాడు. కానీ unused access కూడా risk surfaceనే.
OWASP “Excessive Agency” guidance ప్రకారం agentకు అవసరమైన tools, functions, permissions మాత్రమే ఇవ్వాలి. Read-only taskకి delete లేదా send permission అవసరం లేదు. High-impact action—refund approve చేయడం, customerకి final quotation పంపడం, record మార్చడం—ముందు human approval ఉండాలి.
కిరణ్ reset చేశాడు: FAQ agentకు clean catalogue read access మాత్రమే. Customer dataలో అవసరమైన fields మాత్రమే. Quote draft చేయగలదు; send చేయలేదు. Refund requestను classify చేయగలదు; approve చేయలేదు. ప్రతి actionకు log ఉండాలి. Automationకు keys ఇవ్వడం easy; సరైన doors మాత్రమే తెరవడం discipline.
Mistake 4: “బాగానే ఉంది” తప్ప metric లేకపోవడం
Agent success అంటే ఏమిటి? Faster replyనా? Correct answerనా? Staff time savedనా? Customer issue resolvedనా? కిరణ్ దగ్గర మొదట answer లేదు. Dashboardలో ఎక్కువ conversations కనిపించాయి; business value మాత్రం తెలియలేదు.
అతను నాలుగు practical metrics ఎంచుకున్నాడు:
- Answer accuracy: verified sampleలో correct replies percentage.
- Escalation quality: uncertain cases నిజంగా humanకి వెళ్లాయా?
- Resolution time: customer issue close కావడానికి పట్టిన సమయం.
- Rework rate: employee correction అవసరమైన replies ఎంత?
Metricsకు target, review date, owner లేకపోతే అవి decoration. మొదట small test setతో baseline తీసుకుని, limited pilot తర్వాత compare చేయాలి. “Agent ఎన్ని messages పంపింది?” కంటే “సరైన పని ఎంతవరకు పూర్తయింది?” అనే metric ముఖ్యం.
Mistake 5: “Set and forget” అనుకోవడం
Festival offer మారింది. Supplier catalogue update అయింది. Customers కొత్త ప్రశ్నలు అడిగారు. Agent మాత్రం launch-day instructionsతోనే ఉంది. AI system live చేసిన తర్వాత work ముగియదు; monitoring మొదలవుతుంది.
NIST framework production behaviorను monitor చేయడం, errors మరియు emerging risksను track చేయడం, controlsను regularly reassess చేయడం గురించి స్పష్టంగా చెబుతుంది. కిరణ్ weekly review పెట్టాడు: ten random conversations, every customer complaint, every manual correction. Month-endలో prompt, knowledge source, permissions, metrics review. Change చేసినప్పుడు small test మళ్లీ run.
Perfect agent కోసం కాదు ఈ routine. Drift, stale data, new failure patterns earlyగా కనిపించేందుకు.
Mistake 6: Humanను loop నుంచి పూర్తిగా తీసేయడం
Automation goal “people లేకుండా business” కాదు. Repetitive work తగ్గించి, people judgment అవసరమైన చోట focus చేయడం. Complaintలో emotion ఉంటుంది. Refundలో policyతో పాటు context ఉంటుంది. High-value quoteలో margin, relationship, delivery risk ఉంటాయి.
అందుకే మేఘన మూడు lanes చేసింది:
- Auto-answer: low-risk, verified FAQs మాత్రమే.
- Draft + approve: quotations, order changes, public posts.
- Human only: refunds, sensitive data, disputes, unusual requests.
Agent uncertainty చూపాలి, escalation easyగా ఉండాలి, employee override చేయగలగాలి. Human oversight bottleneck కాదు; high-impact mistakesకు brake.
2026లో ఇంకో layer: agent చదివే content కూడా instruction కావచ్చు
ఇప్పటి agents email, website, PDF, shared document చదివి actions తీసుకోగలవు. అక్కడే indirect prompt injection risk వస్తుంది: బయట నుంచి వచ్చిన contentలో దాగిన instruction agentను అసలు task నుంచి తప్పించవచ్చు. NIST దీనిని agent hijackingగా పరిశీలిస్తోంది; OWASP కూడా prompt injectionను ముఖ్యమైన GenAI riskగా గుర్తించింది.
Small businessకి practical protection ఇలా ఉంటుంది: external contentను trusted instructionగా చూడకండి; payment, delete, send, publish వంటి actionsకు human approval పెట్టండి; agent ఏమి చదివింది, ఏ tool వాడింది, ఏమి మార్చింది అనే audit log ఉంచండి. ఒక రోజుకు actions లేదా spending limit పెట్టండి. Vendor customer dataను ఎంతకాలం ఉంచుతుంది, trainingకు వాడుతుందా, export/delete option ఉందా ముందే తెలుసుకోండి. Agent fail అయితే manual fallback ఎవరు చేపడతారో కూడా రాయండి.
కిరణ్ 30-day pilotలో accuracy, rework, escalation, response timeతో పాటు cost per resolved request మరియు security exceptionsను weeklyగా చూశాడు. Scale చేయాలా వద్దా అన్న decision hypeపై కాదు—ఈ scorecardపై తీసుకున్నాడు.
కిరణ్ second launch: చిన్నది, కానీ నిజంగా ఉపయోగపడింది
రెండోసారి కిరణ్ flashy launch చేయలేదు. ఒక narrow FAQ workflowతో మొదలు పెట్టాడు. Clean source data. Minimum access. Before-send approval. Weekly review. Clear owner. Four metrics.
Agent ఇప్పుడు magicగా business నడపలేదు. కానీ repetitive questionsకి consistent first draft ఇచ్చింది; uncertain requestsను teamకి పంపింది; ప్రతి correction తర్వాత source data improve అయింది. Real win “AI ఉంది” అనే badge కాదు—less avoidable rework, clearer responsibility, safer decisions.
మీ AI agentను live చేసే ముందు 6 ప్రశ్నలు
- ఇది solve చేసే ఒక specific problem ఏమిటి?
- Agent ఉపయోగించే dataకి owner, update date ఉన్నాయా?
- అవసరమైన minimum permissions మాత్రమే ఇచ్చామా?
- Success, failure కొలిచే metrics ఏవి?
- ఎవరు, ఎంత తరచుగా monitor చేస్తారు?
- ఏ actionsకు తప్పనిసరిగా human approval కావాలి?
Bottom line: AI agents magic కాదు; tools. సరైన processలో, clean informationతో, measured guardrails మధ్య, accountable peopleతో పనిచేసినప్పుడే అవి useful systems అవుతాయి.
Sources & fact-check notes
- NIST AI RMF Core: intended scope, human oversight, measurement and lifecycle monitoring
- NIST AI Risk Management Framework 1.0
- OWASP LLM06:2025 Excessive Agency—minimum permissions and human approval
- NIST: evaluating AI agent hijacking and indirect prompt injection
- OWASP LLM01:2025 Prompt Injection
- Google Cloud: agent evaluation using test cases and performance, safety and quality metrics
Educational content only. Security, privacy, compliance and operational controls should be adapted to the specific system, data and applicable requirements. All story characters and outcomes are fictional.